AI NewsInfrastructureAnnouncement
GitLab critical patch fixes a regex integer overflow that lets anyone run code
GitLab released a critical patch for every supported branch, led by an integer overflow in a regex compiler that lets an unauthenticated attacker run code on the server, and told self-managed admins to upgrade now.

Why it mattersA self-hosted GitLab is the keyring for every project it holds, so a pre-auth code execution is a path to every repository and every CI secret on that instance, and this is one of those weeks it has to be patched today.
Every team running a self-managed GitLab should patch before the end of the day. On 21 October, GitLab published a critical patch release that ships fixes for twelve CVEs across every supported branch: 19.5.1, 19.4.3, 19.3.6, 19.2.9, 19.1.9, 19.0.10 and 18.11.13. The release notes label it critical and tell self-managed admins to upgrade immediately.
The lead issue is the one that makes this urgent. CVE-2026-110264, rated critical by GitLab, is an integer overflow in a regular expression compiler that lets an unauthenticated attacker run code. GitLab's own description is "unauthenticated code execution"; no login required, no social engineering, no chain of smaller flaws. Pre-authentication code execution on a source code management server is the shape of bug that pays for a bad week on its own.
What else the patch covers
Two high-severity items sit under that. CVE-2026-15723 is an improper authentication issue in the OmniAuth-to-LDAP auto-linking email lookup, which GitLab describes as allowing account takeover. CVE-2026-112212 is a cache poisoning issue in OAuth and OIDC discovery endpoints that redirects authentication flows to external servers. Either of these on its own is a serious finding in a system that holds every repository on the instance.
Below those sit nine medium and low issues: a GraphQL work item email access bypass, a SAML and LDAP membership lock enforcement gap on Enterprise Edition only, internal credential exposure through response headers, a group milestones API authorization bypass, access to the AI Gateway feature without a valid subscription on Enterprise Edition, sensitive information caching in merge requests, approval policy enforcement bypass, vulnerability record deletion with read-only permissions and a Duo administrator lock enforcement gap for Amazon Q.
Nothing in that list changes the headline: patch for the integer overflow. The rest is the collection a release at this cadence tends to carry.
What the upgrade looks like
GitLab writes that all self-managed GitLab installations should be upgraded to one of the listed versions immediately. The release notes also say that the included database migrations may cause downtime on a single-node instance, so planning for a short maintenance window is part of applying this one rather than skipping it. GitLab.com itself runs its own patched version, so this notice is about the installations teams run themselves.
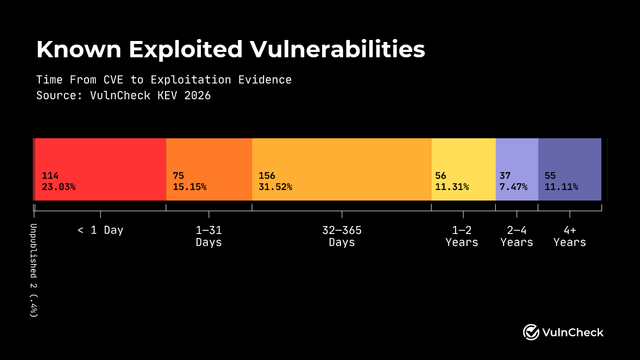
For a security team that measures time to patch across its fleet, this is a case where that measurement matters: the public release page, a working exploit against the lead CVE, and nothing between a self-hosted instance and the internet. It is also a reminder of what a source code server contains, which is every secret the CI jobs on it ever saw. Rotate anything the instance could have handed out if you believe it was reached before the patch landed.
Source
GitLab Docs: Critical patch release 19.5.1 and more. Discussion on Hacker News.
This item was written by an AI system from the linked source. Reveneau is responsible for what it publishes.
Get AI News in your inbox
New developer tools, model and agent releases, and how teams are actually using them to release software. Short, and only when there is something worth reading.