Image: GitHub
Why it mattersTeams already paying for Advanced Security get a second column of advisory findings on every pull request, with no Copilot licence needed to turn it on.
A pull request in a modern codebase usually touches a Dockerfile, a Terraform plan or a shell script, and GitHub's code scanner reads none of them. GitHub says that gap is now covered by a second scanner that runs on the same pull-request event and lists its results on the same tab.
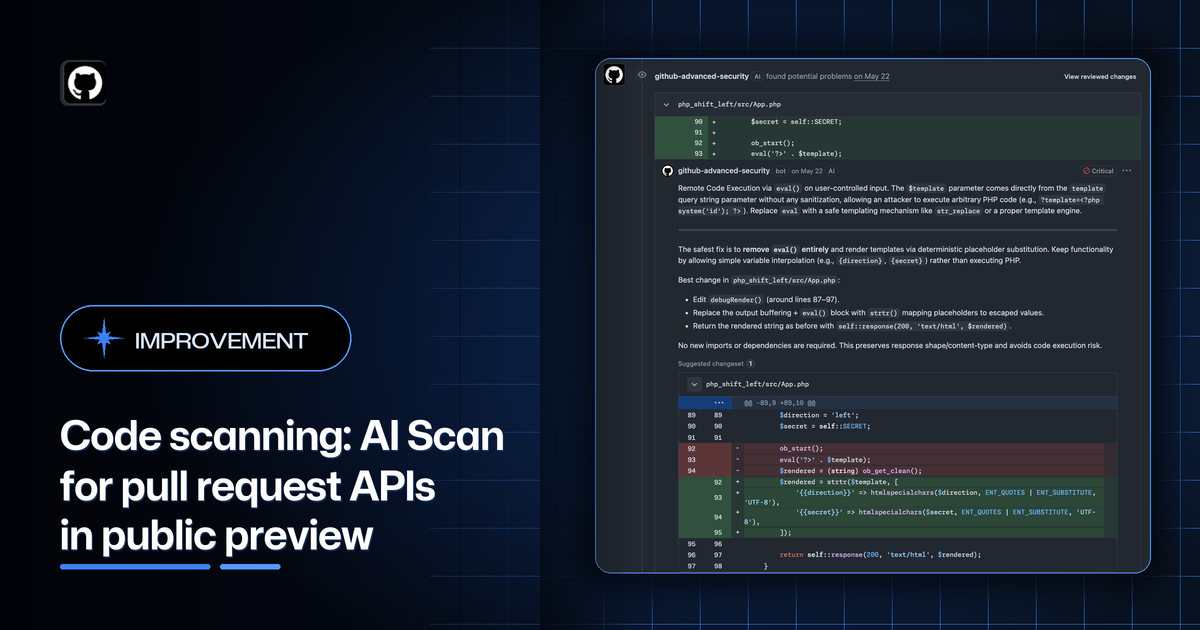
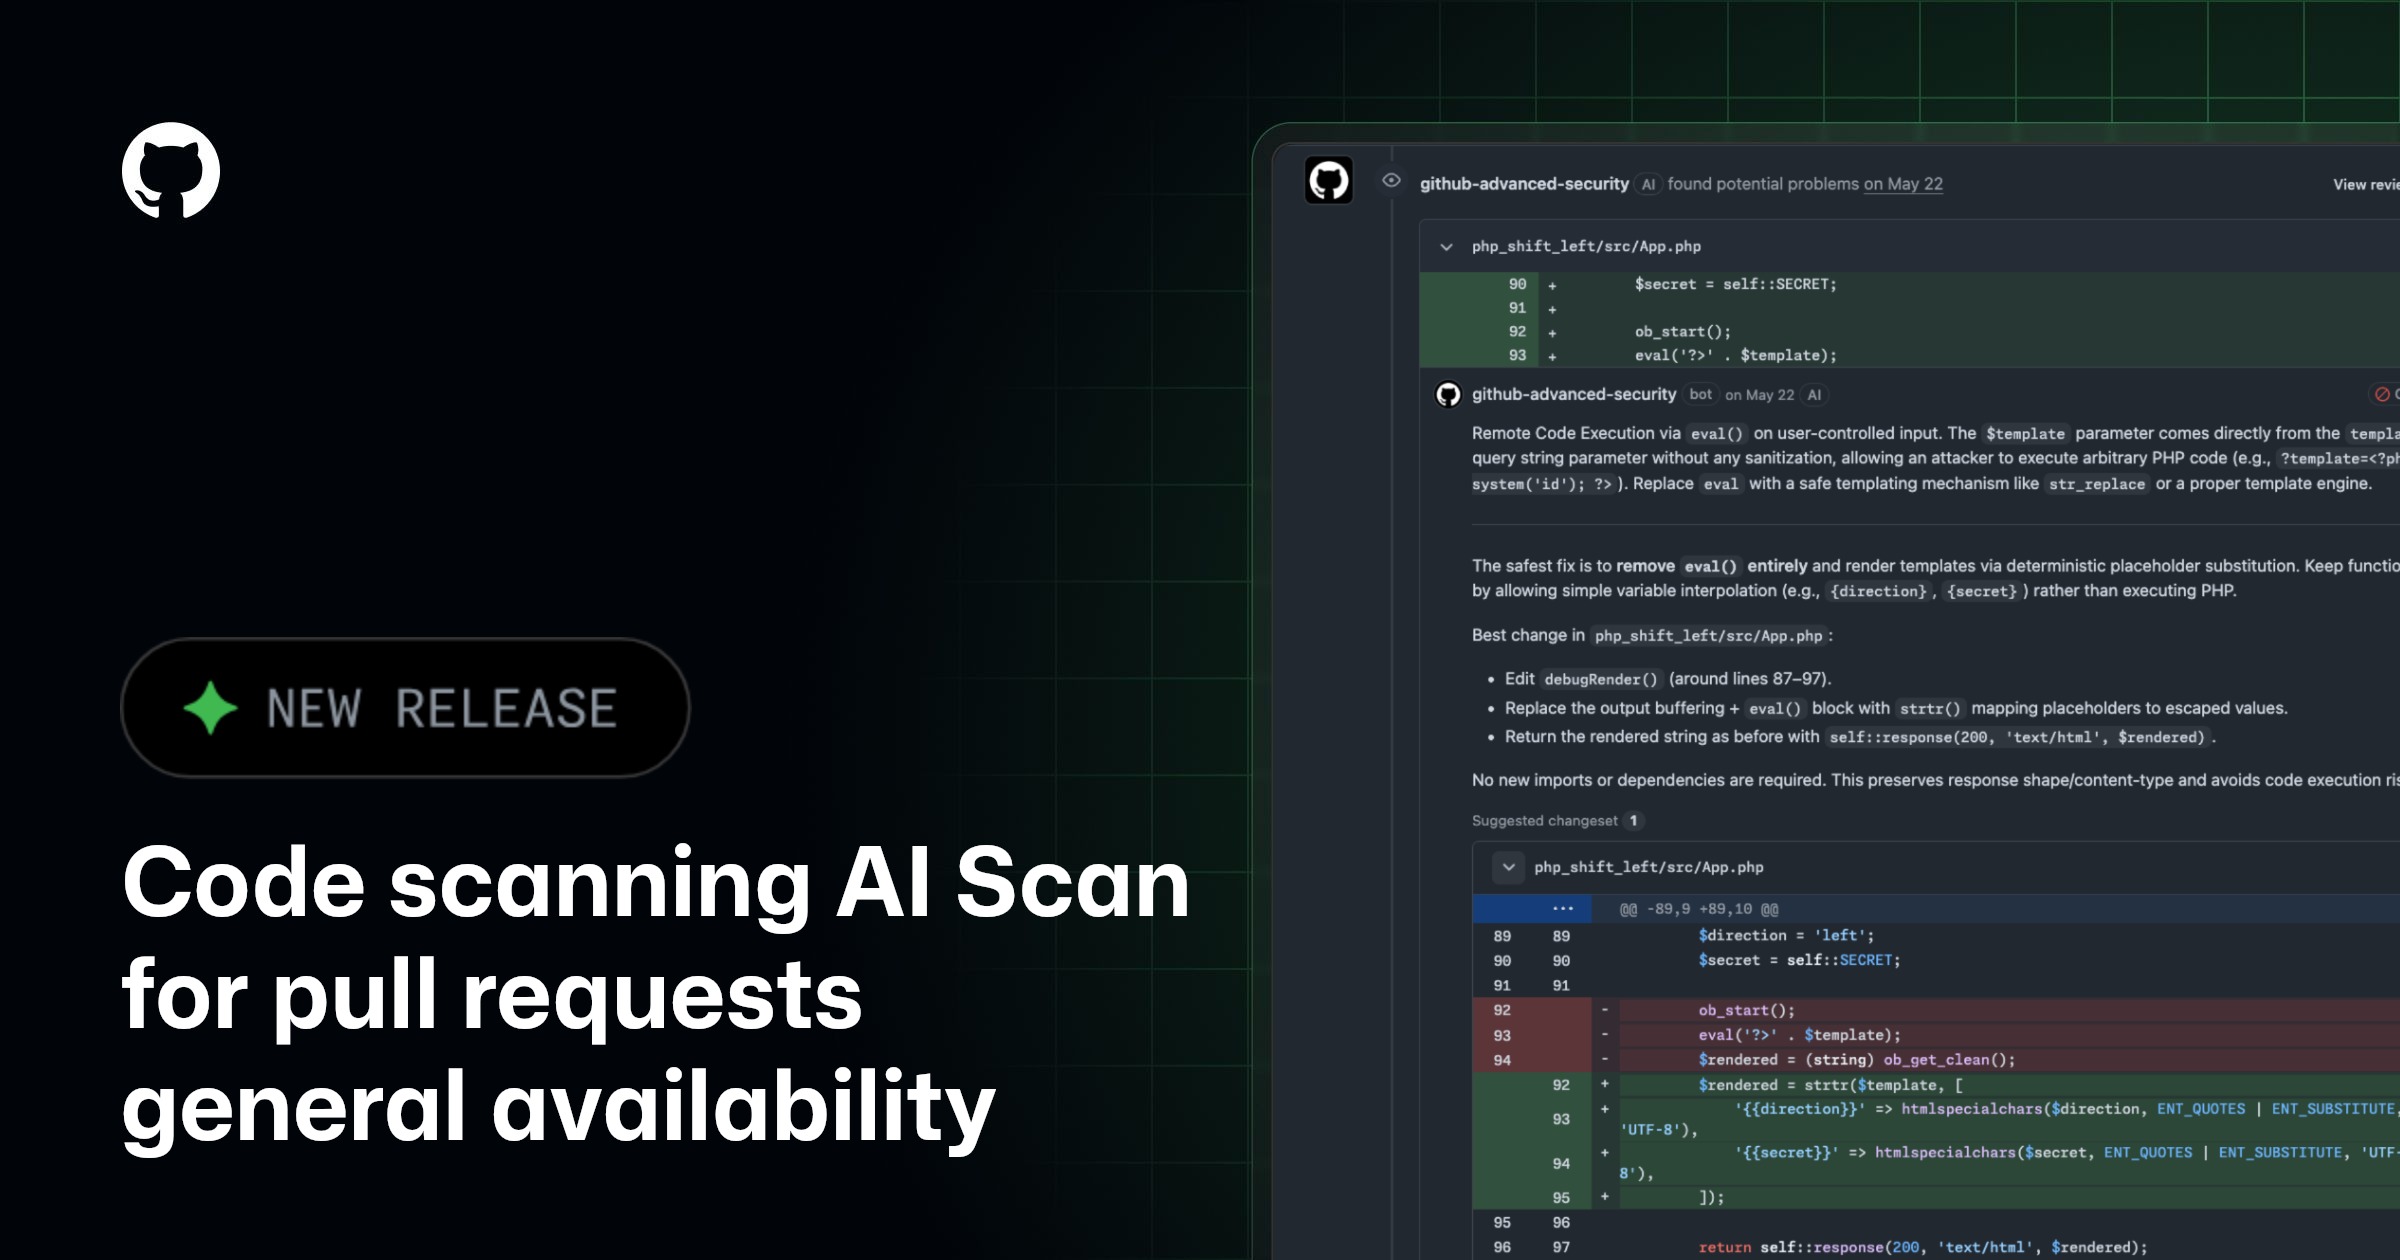
AI Scan for pull requests is now generally available, GitHub says. It covers the languages CodeQL does not: PHP, Shell/Bash, Terraform configuration (HCL), Dockerfiles, JSP for Java, Blazor for C# and others. Its results appear next to CodeQL's on the Conversation and Files changed tabs, with an "AI" indicator on each finding.
What a developer sees
An AI Scan finding carries an explanation of the security risk and a suggested autofix. GitHub says the results are advisory: they do not fail the code scanning check and cannot block a pull request merge through a ruleset requirement. AI Scan does not run on pull requests from forks, and it does not run on pull requests created by Dependabot.
Who can turn it on
GitHub says AI Scan is free on public repositories owned by organizations or personal accounts. For private and internal organization-owned repositories, GitHub Code Security or GitHub Advanced Security is required. A GitHub Copilot licence is not required, so a team that pays for Advanced Security without using Copilot can still turn this on.
How it is billed
Each run of AI Scan consumes Code Security AI Credits, which GitHub lists under the "Advanced Security" product in the AI usage section of enterprise billing and licensing. A team can set SKU-level budgets for those credits, so a repository that opens many pull requests in one month cannot drive the bill past a limit the team has set.
GitHub makes no claim about false positive rate, no benchmark against CodeQL, and no measurement of how often the suggested autofix is accepted. The advisory-only default is the honest signal here: if GitHub were confident enough to let AI Scan block a merge, the changelog would say so.
For a team already paying for Advanced Security, turning this on is one setting at the organization level and a second column of findings on the pull-request Conversation tab. For a public repository, it is free and automatic once code scanning is enabled. The question each team will answer in the first few weeks of output is whether the extra advisory lines help a reviewer catch something real, or whether they add work for no change in what gets fixed.
Source
This item was written by an AI system from the linked source. Reveneau is responsible for what it publishes.
Get AI News in your inbox
New developer tools, model and agent releases, and how teams are actually using them to release software. Short, and only when there is something worth reading.